KEY INSIGHTS
- The maximum number of passphrases for the Trezor can be increased up to 128 characters thanks to new firmware.
- Unique passphrases helped some users of the Coldcard to protect their funds from being stolen during the theft of around $116 million.
- The Trezor recommends that CryptoBilis users withdraw their funds because of concerns about hardware implants.
The Trezor extended the optional wallet passphrase limit to 128 characters after a serious security problem with Coldcard hardware wallets that led to the loss of about $116 million of Bitcoin.
The November 1 announcement introduces the expanded limit through Trezor Suite, requiring users to install updated device firmware to access the feature. The company said strong, unique passphrases helped protect some Coldcard users affected by the July attacks, highlighting the additional protection offered by a separate wallet password.
The development comes shortly after Trezor issued a security warning to customers who purchased devices through former authorized reseller CryptoBilis. The warning followed a report of a suspected hardware implant inside a Trezor Safe 5, raising separate concerns about the security of devices obtained through the reseller.
Increase in Trezor Passphrase Character Limit Post-Firmware Update
The latest firmware update by Trezor in October 2026 provides the extended passphrase feature with the character limit going up from 50 to 128. The company confirmed the change in its November 1 announcement, explaining that users must update their device firmware before accessing the expanded functionality. Devices operating on older firmware will continue supporting the previous character limit.
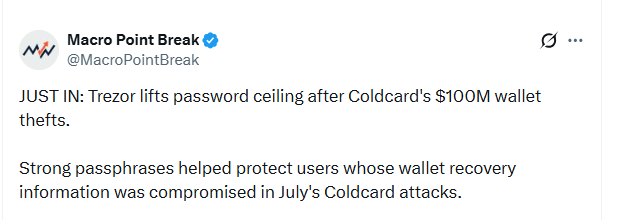
Source: Macro Point Break
The expanded allowance does not cover every device model. As per the new documentation by Trezor, the Model T, Safe 3, Safe 5 and Safe 7 models allow passphrases with a maximum of 128 characters while the Model One continues to have the 50-character limit.
A passphrase is an optional secret that one uses together with their wallet backup which may also be called a recovery phrase or seed. Each passphrase will give access to a unique wallet containing its own set of addresses, balance and transaction history. In case someone gets hold of your recovery phrase, they will need to know the passphrase for you to access your funds.
Trezor advises that users should ensure that the secret is safe since they do not keep a copy of it and their support team cannot restore or reset the passphrase. Entering a different passphrase means accessing a different wallet.
Exploit on Coldcard Revealed Importance of Passphrase Protection
Trezor linked the expanded character limit to the Coldcard incident in July 2026. TRM Labs reported that attackers began draining affected Bitcoin wallets on July 30, exploiting a firmware flaw associated with a March 2021 release.
A build configuration error caused some devices to generate wallet seeds using a weaker software random-number generator rather than the intended hardware-based source.
TRM estimated that attackers took approximately 1,816 BTC, worth about $116 million at the time of its analysis, from more than 5,200 addresses across four waves.
Trezor said some affected Coldcard users avoided losses in the first wave because they had strong, unique passphrases. Attackers needed both the compromised backup and the additional secret to reach those wallets, according to the company.
The measure allowed certain individuals to shift their funds, showing how an extra layer of security can be offered by a passphrase once the recovery phrase becomes known.
The firm used the case as a way of explaining why users may need longer passphrases. The increased number of characters allows for more leeway for users who want to have complex wallet passwords.
Separate Warning Follows Suspected CryptoBilis Implant
On October 30, Trezor urged customers who purchased wallets from former authorized reseller CryptoBilis from March 2026 onward to transfer their funds to newly created wallets. The warning followed an Indonesian customer’s report of a suspected unauthorized circuit board inside a Trezor Safe 5 bought through Tokopedia in August.
The customer said the additional board sat between the wallet’s main circuit board and screen and included a cellular module and antenna. It could reportedly capture information displayed on the screen, including recovery phrases, and transmit it over a mobile network. These capabilities remain allegations based on the customer’s report; Trezor has not completed a laboratory examination.
Trezor told Cointelegraph it had not received the device for inspection and had no reports of related customer losses. Chief commercial officer Danny Sanders said the company was treating the report as credible and chose to warn customers before completing its examination.
The warning followed reports involving tampered Ledger devices sold through the same reseller. Trezor had also stopped sales through CryptoBilis on October 9.
Frequently Asked Questions
What is Trezor’s new maximum passphrase length?
Trezor has increased its optional wallet passphrase limit from 50 to 128 characters on supported devices running updated firmware.
Why did Trezor increase the passphrase limit?
The corporation’s post from July 2026, about the Coldcard hack, also highlighted the firmware vulnerability and noted that some users’ wallets were secured by strong and unique passphrases.
Coldcard hack: How much Bitcoin was stolen?
TRM Labs says more than 5,200 addresses were used to steal about 1,816 BTC ($116 million).